Written by: Chief Executive Officer
Oleg SadikovUpdated: 12.10.2026
23 min read
Software teams are releasing more frequently, yet quality engineering often struggles to keep pace. The World Quality Report 2025–26 found that only about one-third of test cases are automated, quality engineering is fully integrated into just 20% of Agile teams, and only 25% of organizations connect quality metrics to business outcomes.
Testing as a Service, or TaaS, gives companies another way to close these gaps. Instead of building every testing capability internally, a business obtains the expertise, environments, tools, and testing capacity it needs from a specialized provider.
However, TaaS is not simply a more elaborate name for outsourcing testers. When implemented properly, it is a structured service with defined objectives, workflows, deliverables, performance indicators, and responsibilities.
This guide explains how Testing as a Service works, what it can include, when it makes sense, and how to select and integrate a TaaS provider.
What is Testing as a Service?
Testing as a Service is a delivery model in which an external provider supplies software testing capabilities on demand or as an ongoing managed service.
Depending on the agreement, the provider may handle:
Test planning and estimation;
Manual functional testing;
Test automation;
Regression testing;
API and integration testing;
Performance and scalability testing;
Security testing;
Mobile and cross-platform testing;
Accessibility and usability testing;
Test environments and test data;
Quality reporting and release recommendations.
The company retains ownership of its product and business decisions. The TaaS provider takes responsibility for an agreed part of the testing process.
For example, a SaaS company may keep exploratory and acceptance testing inside its product teams while asking a TaaS provider to maintain regression automation, test APIs, and run performance tests before major releases.
TaaS can therefore supplement an internal team, replace a missing specialist capability, or operate as a managed testing function.
Is TaaS the same as software testing outsourcing?
TaaS is a form of software testing outsourcing, but the terms are not always interchangeable.
Traditional outsourcing may simply mean hiring an external tester or team. Testing as a Service normally describes a more structured arrangement in which the customer purchases a defined testing capability or outcome.
A TaaS agreement should specify:
Scope and testing responsibilities;
Expected deliverables;
Service levels and response times;
Required environments and integrations;
Reporting frequency;
Quality and delivery metrics;
Pricing and scaling rules;
Security and access controls.
The distinction matters because adding testers does not automatically solve an ineffective testing process. A useful TaaS model combines people, processes, tools, and accountability.
How does Testing as a Service work?
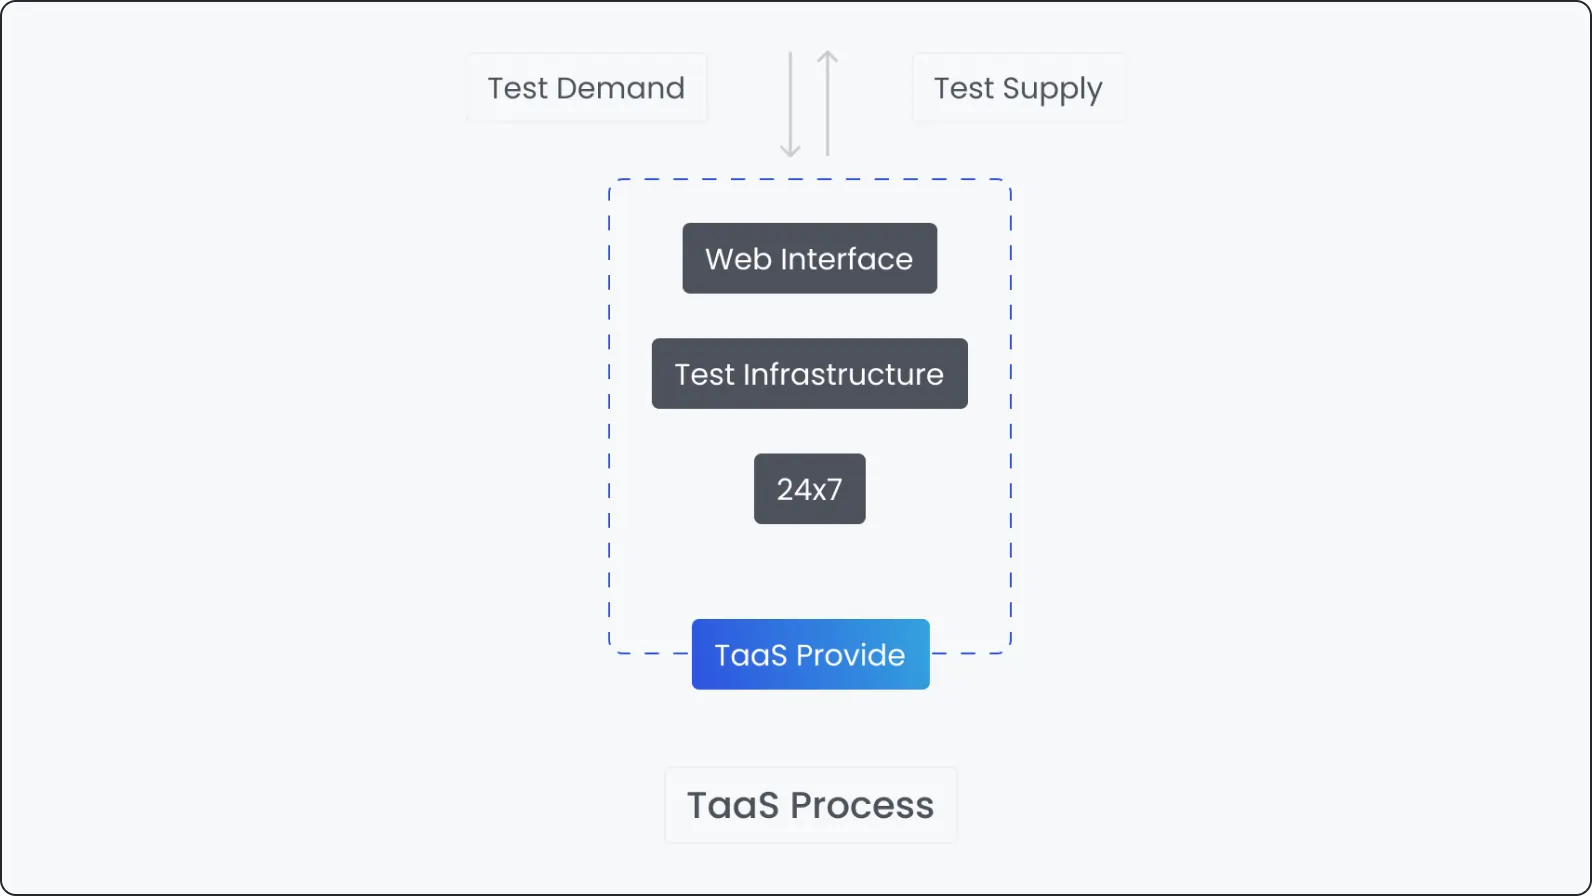
A TaaS engagement usually begins with an assessment of the product, release process, technology stack, risks, and current QA maturity.
The provider then defines the service scope. This might be a narrowly focused service, such as an independent security assessment, or a broader continuous testing function integrated into the development lifecycle.
A typical workflow includes five stages.
1. Discovery and assessment
The provider reviews the product architecture, requirements, existing test assets, defect history, environments, release cadence, and business-critical user journeys.
The purpose is to identify where testing can reduce the most risk – not simply where more test cases can be created.
2. Service design
The customer and provider agree on:
Testing scope;
Team composition;
Testing environments;
Tools and integrations;
Communication channels;
Entry and exit criteria;
Deliverables;
KPIs and service levels.
Responsibilities should be documented using a model such as RACI so that defects, environment failures, release approvals, and production incidents always have clear owners.
3. Environment and data setup
The provider receives controlled access to the required applications, repositories, test environments, devices, APIs, and project management systems.
Test data deserves particular attention. According to the World Quality Report 2025–26, 60% of organizations struggle to create secure, scalable test data. A TaaS provider should therefore explain how it creates, anonymizes, refreshes, stores, and removes test data.
4. Test execution and integration
Testing may be performed manually, automatically, or through a combination of both. Results should flow into the customer’s existing tools rather than remain isolated in a provider-controlled report.
For continuous delivery, the provider can integrate automated checks into CI/CD pipelines, while manual testers focus on exploratory, usability, and risk-based testing.
5. Reporting and continuous improvement
A mature TaaS provider does more than report test execution numbers. It analyzes defect patterns, unstable product areas, test effectiveness, release risks, and recurring delivery bottlenecks.
The service should evolve as the product changes. Tests that no longer protect meaningful risks should be removed or redesigned instead of being maintained indefinitely.
What services can TaaS include?
Functional testing
Whether features behave according to requirements
New features, frequent releases, complex workflows
Regression testing
Whether recent changes have damaged existing functionality
Products with regular updates and growing test suites
Test automation
Repeatable checks executed with tools and pipelines
Stable, frequently repeated regression scenarios
API testing
Data exchange, business rules, errors, authentication, and contracts
Microservices, mobile backends, third-party integrations
Performance testing
Response times, throughput, scalability, and stability
Traffic growth, campaigns, migrations, major releases
Security testing
Vulnerabilities, access controls, data exposure, and attack surfaces
Products handling sensitive, financial, or health data
Compatibility testing
Behavior across browsers, operating systems, devices, and versions
Web and mobile products with diverse user environments
Usability testing
Whether users can complete important tasks effectively
Consumer products, onboarding flows, checkout, forms
Accessibility testing
Conformance with accessibility requirements and inclusive use
Public-facing and regulated digital services
Compliance testing
Product controls and evidence related to applicable standards
Fintech, healthcare, enterprise, and regulated software
Localization testing
Language, formats, layouts, and regional behavior
Products entering new geographic markets
UAT support
Readiness for business and end-user acceptance
Enterprise releases and workflow-heavy systems
Modern applications rarely need only one of these capabilities. APIs are a good example: the Postman 2025 State of the API Report found that testing is performed by 81% of API professionals. Yet while functional and integration testing each reached 67%, contract testing was used by only 17%. A specialized provider can help close gaps that a general development team may not have the time or expertise to address.
TaaS vs QAaaS vs TAaaS
The terminology is not standardized across the industry. Some vendors use TaaS and QAaaS interchangeably, so buyers should evaluate the actual scope rather than rely on the acronym.
A practical distinction looks like this:
TaaS — Testing as a Service
Executing and managing software testing
Manual testing, automation, performance, security, compatibility, API testing, test reporting
Companies that need scalable testing capabilities
QAaaS — Quality Assurance as a Service
Improving quality across the software lifecycle
QA strategy, governance, process design, quality coaching, testing, metrics, release controls
Companies that need broader quality ownership and process transformation
TAaaS — Test Automation as a Service
Building and operating automated testing
Framework setup, script development, CI/CD integration, maintenance, reporting
Teams with repetitive regression work or automation skill gaps
TaaS is the broad testing delivery model. TAaaS is its automation-focused subset. QAaaS usually extends beyond test execution to include prevention, governance, development practices, and quality management.
Read more about integrating QA as a Service or explore the narrower Test Automation as a Service model.
Types of TaaS providers
Not every provider offers the same depth of expertise or level of ownership. Most fall into one of the following categories.
Specialized software testing companies
These providers focus primarily on QA and quality engineering. They typically offer a broad range of manual, automated, performance, security, mobile, and specialized testing services.
A specialized company is often suitable when testing quality, independence, and access to multiple QA disciplines matter more than receiving all IT services from one vendor.
Full-service technology vendors
Large development and consulting firms may include testing within a broader engineering engagement. This can reduce the number of vendors involved, although testing may not be the provider’s central competency.
The model can work well for large transformation programs where development, infrastructure, integration, and testing are managed together.
Niche testing specialists
Some providers concentrate on areas such as penetration testing, accessibility, performance engineering, ERP testing, mobile devices, payment systems, or regulatory compliance.
They are valuable when a product needs deep expertise for a clearly defined risk. A niche provider may work alongside an internal QA team or a general TaaS partner.
Cloud testing platforms
These services provide on-demand browsers, mobile devices, infrastructure, or automated test execution environments. They offer technology and capacity but may provide limited human-led testing or quality management.
A platform can be one component of TaaS, but access to testing infrastructure alone is not the same as a managed testing service.
Staff augmentation providers
Staff augmentation gives a company additional QA engineers who work under its internal management. It offers direct control but leaves planning, tools, priorities, and results with the customer.
This model is appropriate when the testing process already works and the primary problem is temporary capacity.
Managed testing providers
A managed provider assumes responsibility for an agreed testing function and its results. It may supply a team, test leadership, tools, processes, automation, reporting, and continuous improvement.
This model requires more initial alignment but reduces the customer’s day-to-day management burden.
TaaS engagement models
On-demand or project-based TaaS
Testing is purchased for a particular release, migration, audit, or product milestone.
It works well for:
Pre-release regression;
Independent product assessment;
Performance testing before a traffic peak;
Security or accessibility audits;
Short-term specialist requirements.
The limitation is continuity. A short engagement gives the provider less time to learn the product and build reusable knowledge.
Dedicated testing team
A stable external team works with the customer over an extended period. The customer usually retains control over priorities and daily work.
This model provides continuity and domain knowledge while avoiding permanent internal hiring.
Managed testing service
The provider owns defined testing outcomes, processes, staffing, and reporting. Performance is evaluated against agreed KPIs or service levels.
Managed TaaS is most effective when the scope is stable enough to define but broad enough to justify provider ownership.
Hybrid TaaS
Internal and external specialists share testing responsibilities. For example, the internal team may own product acceptance and exploratory testing, while the provider handles automation, regression, compatibility, and performance testing.
For many organizations, this is the most practical model because it combines internal product knowledge with external testing depth.
Benefits of Testing as a Service
Access to specialized expertise
Maintaining internal experts in every QA discipline is expensive and often unnecessary. TaaS provides access to specialists when their knowledge is required.
This is increasingly relevant as testing expands beyond UI checks. Quality engineers may need skills in APIs, cloud infrastructure, observability, security, accessibility, performance, AI systems, and test data engineering.
Flexible testing capacity
Testing demand is rarely constant. It can increase sharply before releases, migrations, seasonal campaigns, or compliance deadlines.
TaaS enables a company to expand or reduce capacity without treating every temporary workload increase as a permanent hiring requirement.
Faster feedback
Providers with established processes and reusable infrastructure can begin testing faster than a company building a new QA capability from scratch.
Speed should still be measured carefully. The objective is not simply to execute more tests, but to deliver useful information early enough to change a development or release decision.
Broader coverage
An external provider can test across additional devices, environments, integrations, data conditions, and user scenarios.
This is particularly valuable for mobile products, globally distributed systems, and applications that depend on numerous third-party services.
Independent product assessment
An external team can challenge assumptions that have become invisible to people working on the product every day. This independence is valuable before important releases, acquisitions, migrations, and regulatory reviews.
More predictable costs
TaaS can convert parts of the QA function into a planned service expense. However, savings are not automatic. They depend on scope stability, onboarding costs, internal coordination, tooling, and the amount of rework.
The correct comparison is total cost and risk – not simply the hourly rate of an internal and external tester.
When should you use Testing as a Service?
TaaS is worth considering when one or more of the following conditions apply.
Your release schedule has outgrown the QA team
If testing repeatedly becomes the final release bottleneck, external capacity can help. But the provider should also identify why the bottleneck exists: slow environments, unclear requirements, excessive regression suites, unstable builds, or missing automation.
You need expertise that is difficult to maintain internally
Performance, accessibility, security, mobile device coverage, and test automation architecture often require specialists who may not be needed full-time.
TaaS allows these capabilities to be introduced without creating a permanent role for every discipline.
Testing demand changes significantly
Businesses with seasonal traffic, project-based releases, or rapid growth need a model that can scale without repeated hiring and downsizing.
You are launching a new product or platform
A TaaS provider can help establish a test strategy, define critical coverage, prepare environments, and assess release readiness while the internal team remains focused on product development.
You are modernizing a legacy system
Legacy modernization creates risks across old and new interfaces, data migration, integrations, and business processes. Independent testing can provide continuity while architecture changes.
You need an objective quality assessment
An external provider is useful when management, investors, customers, or regulators require an independent view of product quality.
You want to introduce continuous testing
According to Postman, 75% of organizations use CI/CD pipelines. Yet automation inside a pipeline is only useful when tests are fast, stable, relevant, and correctly maintained.
CircleCI’s aggregated workflow data illustrates the gap between typical and leading delivery performance: the median workflow success rate is 69.24%, compared with 90% for the top 5% of teams. These are CI workflow figures rather than test-specific results, but they show why pipeline reliability and rapid feedback deserve attention.
A TaaS provider can help design testing around the delivery pipeline instead of simply moving an old regression suite into CI.
When TaaS may not be the right choice
Testing as a Service is not a universal solution.
It may provide limited value when:
The product is too early and changes completely every few days;
Testing requirements cannot yet be defined;
No internal owner can prioritize risks or answer product questions;
Security policies prevent any workable form of external access;
The expected engagement is too small to justify onboarding;
The company wants to outsource accountability for product quality entirely.
The final point is critical. A provider can own testing activities and agreed service outcomes, but product quality remains a shared responsibility across product, engineering, operations, and business teams.
TaaS also performs poorly when used to compensate for chronically unclear requirements, unstable environments, or builds that are not testable. These problems should be addressed as part of the engagement rather than hidden behind additional test execution.
How to implement TaaS step by step
Step 1: Define the business outcome
Start with the problem, not the number of testers required.
A useful objective might be:
Reduce regression feedback from three days to six hours;
Validate release readiness across supported devices;
Establish performance limits before a campaign;
Reduce production defects in payment workflows;
Introduce API contract testing;
Provide independent evidence for a compliance review.
This makes the provider accountable for relevant results.
Step 2: Establish a baseline
Measure the current situation before the service begins. Possible baseline metrics include regression duration, escaped defects, test stability, environment downtime, release delays, and time spent fixing test failures.
Without a baseline, it will be difficult to determine whether TaaS has improved anything.
Step 3: Select the service and engagement model
Decide whether you need an assessment, a specialist project, additional engineers, a dedicated team, or a fully managed testing function.
Choose the smallest model that can address the actual problem. It can be expanded after the provider demonstrates value.
Step 4: Run a controlled pilot
Use a representative but limited scope: one product area, platform, test level, or release stream.
The pilot should test not only technical skills but also communication, reporting, domain learning, security procedures, and cooperation with developers.
Step 5: Establish access and security controls
Define what the provider can access, how accounts are approved, where test data is stored, and how access is removed.
Use least-privilege access, separate testing environments, audit logs, multifactor authentication, data masking, and contractual data-handling requirements where applicable.
Step 6: Integrate the provider into delivery workflows
External testing should not become a separate queue at the end of development. Include the provider in planning, requirement reviews, defect triage, risk discussions, and release preparation.
The earlier testers understand a change, the more effectively they can prevent rather than merely detect problems.
Step 7: Agree on metrics and governance
Define how frequently results will be reviewed, who can change priorities, how risks are escalated, and how service improvements are approved.
Avoid measuring success only through executed test cases or detected defects. These figures can encourage volume without demonstrating value.
Step 8: Scale deliberately
Expand the service only after the pilot produces stable workflows, useful metrics, and clear ownership.
Document knowledge throughout the engagement so that the company does not become dependent on particular individuals or a proprietary process.
How to choose a TaaS provider
Relevant technical expertise
Evaluate whether the provider understands your architecture, delivery model, platforms, integrations, and testing requirements.
Ask for concrete explanations of how it would test your product rather than accepting a generic list of tools.
Domain knowledge
A technically correct test can still miss the most important business risk. Providers working with financial, healthcare, enterprise, or regulated products should understand the workflows and constraints of that domain.
Service scope
Determine whether the provider offers only test execution or can also support planning, environments, data, automation, reporting, and process improvement.
The scope should match the problem you are trying to solve.
Security practices
Review security certifications, employee access procedures, device management, data handling, incident response, and subcontractor policies.
Security deserves particular attention when production-like data or sensitive intellectual property is involved.
Integration capabilities
The provider should be able to work with your issue tracker, source control, CI/CD pipelines, communication tools, test management system, and reporting environment.
Avoid a service that creates a disconnected testing process.
Automation and AI maturity
Ask how the provider selects automation candidates, handles flaky tests, maintains frameworks, validates AI-generated test assets, and protects customer data.
AI branding alone is not evidence of maturity. The World Quality Report found that 43% of organizations were experimenting with generative AI in QA, but only 15% had scaled it enterprise-wide. Providers should be able to explain governance, validation, and measurable outcomes – not just tool adoption.
Transparency
You should retain visibility into:
Test assets;
Execution results;
Defects;
Risks;
Team capacity;
Automation stability;
Service costs;
Improvement plans.
Avoid arrangements in which the customer receives only a periodic summary without access to the underlying evidence.
Scalability and continuity
Ask how quickly the provider can increase capacity, how new engineers are onboarded, and how knowledge is retained when team members change.
Exit and knowledge-transfer provisions
The contract should describe who owns test scripts, frameworks, documentation, environments, and data. It should also define how these assets will be transferred at the end of the engagement.
TaaS challenges and how to manage them
Slow domain onboarding
Testers may miss business-critical risks
Provide workflow documentation, access to product experts, and structured domain training
Fragmented ownership
Defects and release decisions can fall between teams
Define responsibilities and escalation paths before execution begins
Data security
Testing may expose customer or production-like data
Mask data, enforce least privilege, audit access, and define retention rules
Vendor dependency
Knowledge and assets may become difficult to transfer
Require shared repositories, documentation, and regular knowledge transfer
Hidden costs
Environments, devices, tools, onboarding, and rework may fall outside the base fee
Define assumptions, exclusions, and change-control rules in the contract
Tool lock-in
Proprietary frameworks can make switching providers expensive
Prefer portable assets and clarify ownership
Communication delays
Distributed teams can lose context or delay decisions
Set overlap hours, response expectations, and documented workflows
Misleading metrics
High test counts may hide poor risk coverage
Use outcome-based metrics connected to releases, users, and business risks
Unstable environments
Test results become unreliable
Track environment health separately and define who resolves infrastructure issues
TaaS pricing models
Time and materials
The customer pays for the time used by the provider’s specialists.
This model works for changing scope, early-stage products, exploratory work, and engagements where the required effort is difficult to estimate.
Fixed-price project
The provider delivers a defined scope for an agreed price.
It is suitable for assessments and testing projects with stable requirements, clear deliverables, and limited dependencies.
Dedicated capacity
The customer reserves a defined team or amount of testing capacity each month.
This model works well for continuous product development and gives better continuity than purely on-demand testing.
Managed service fee
The provider charges for ownership of an agreed testing function, often with service levels and performance targets.
It is appropriate when both sides can define responsibilities and expected outcomes clearly.
Usage-based pricing
Charges are connected to consumption, such as test execution time, devices, environments, transactions, or testing cycles.
Usage pricing can be flexible, but the measurement unit must be transparent. Otherwise, the invoice may grow without a corresponding improvement in quality.
Hybrid pricing
Many TaaS engagements combine a stable monthly fee with separate charges for specialist or peak-demand work.
This offers predictable baseline costs while preserving the ability to scale.
How to measure TaaS performance
The best metrics depend on the service objective. A useful scorecard may include:
Escaped defects by severity;
Defect detection before release;
Regression cycle duration;
Time from build availability to test feedback;
Automated test stability;
Defect reopen rate;
Requirement or risk coverage;
Environment availability;
Release delay caused by quality issues;
Production incident rate;
Time to reproduce and diagnose failures;
Cost per release or testing cycle.
Coverage figures should always state what is being covered: requirements, risks, code, platforms, workflows, or configurations. A standalone percentage can create false confidence.
The industry still has room to improve here. The World Quality Report found that only 25% of organizations connect quality engineering metrics directly to business outcomes. It also reported that 94% review production data, while nearly half struggle to translate those insights into actionable quality improvements.
A strong TaaS provider should help close that loop. Production incidents, customer support trends, failed transactions, performance telemetry, and user behavior should influence what gets tested next.
Testing as a Service checklist
Before signing a TaaS agreement, confirm that you can answer the following questions:
What business or delivery problem should the service solve?
Which testing responsibilities remain internal?
Which responsibilities belong to the provider?
What products, platforms, environments, and integrations are in scope?
Who owns the test strategy and release recommendation?
Which tools and repositories will be used?
Who owns the created test assets?
How will sensitive data be protected?
How will access be granted and revoked?
What service levels and response times apply?
Which quality and business metrics will be tracked?
How will scope and pricing changes be approved?
How will knowledge be documented and transferred?
What happens when the engagement ends?
If these questions remain unanswered, the service is not yet defined well enough to manage.
Final thoughts
Testing as a Service works best when it provides more than additional hands. It should create a dependable testing capability with clear ownership, useful feedback, measurable outcomes, and access to expertise that the company cannot efficiently maintain on its own.
The model is especially valuable when testing demand changes, specialist skills are missing, releases are being delayed, or internal teams need an independent view of product risk.
Success still depends on preparation. Define the outcome, establish a baseline, select the right engagement model, run a controlled pilot, protect access and data, and connect testing metrics to business results.
If you need scalable manual and automated testing without building every capability internally, explore DeviQA’s software testing as a service.
A QA partner for every stage
Frequently asked questions
What does TaaS stand for?
TaaS stands for Testing as a Service. It is a model in which a third-party provider supplies testing expertise, capacity, tools, environments, or management as an on-demand or ongoing service.
What is included in Testing as a Service?
TaaS may include manual functional testing, regression testing, automation, API testing, performance testing, security testing, compatibility testing, accessibility, test environments, data management, and quality reporting. The exact scope depends on the agreement.
What is the difference between TaaS and QAaaS?
TaaS focuses primarily on testing activities. QAaaS usually has a broader scope that may include quality strategy, governance, process improvement, prevention, release controls, and testing across the development lifecycle.
Vendors do not always use the terms consistently, so the documented scope matters more than the label.
Is TaaS only for companies without an internal QA team?
No. TaaS can support companies with established QA teams by adding capacity, independent assessment, infrastructure, or specialist expertise.
Hybrid arrangements are common because internal testers retain product knowledge while an external provider handles specific testing areas.
Can TaaS include test automation?
Yes. Automation can be one part of a broader TaaS engagement. If automation is the primary service, the model may be described more specifically as Test Automation as a Service.
Is Testing as a Service suitable for startups?
It can be useful for startups that need testing expertise but are not ready to build a complete internal QA department. The service should begin with product-critical risks and a focused scope rather than an oversized test process.
How long does it take to implement TaaS?
A narrowly defined assessment may begin within days, while a managed testing service can require several weeks for discovery, access setup, knowledge transfer, environments, workflows, and baseline measurements.
The timeline depends on product complexity, security requirements, existing documentation, and service scope.
How much does TaaS cost?
Cost depends on the engagement model, team composition, testing types, product complexity, tools, environments, and required coverage. Common models include time and materials, fixed-price projects, dedicated capacity, managed service fees, usage-based pricing, and hybrid arrangements.
Does a TaaS provider make the release decision?
Usually, the provider supplies test evidence and a release recommendation. Final approval remains with the customer’s authorized product, engineering, or business stakeholders unless a different governance model is explicitly agreed.
About the author
Chief Executive Officer
Oleg Sadikov is the Chief Executive Officer and co-founder of DeviQA. He founded the company with a clear vision: to raise the bar for digital product quality and make QA a true business enabler, not a checkbox in the delivery process.